The internet is a fantastic tool, but the technical side can feel daunting. That’s why we started this 101 series to break down the fundamentals of the web so you can understand how it all works.
Today’s topic is DNS: a term that gets thrown around constantly but is understood by surprisingly few. By the end of this guide you’ll know what DNS does, what the main record types are for, and how to manage your own. Let’s get started.
What does DNS mean?
DNS stands for Domain Name System. Its job is to translate domain names that people can remember (like yourbusiness.com.au) into the IP addresses that computers actually use to find each other (like 115.178.16.48).
Think of it as the internet’s contacts app. You don’t memorise your friends’ phone numbers, you look up their name and your phone dials the right number. DNS does exactly that for websites and email: you type a name, and DNS supplies the number behind it.
Why does DNS matter?
DNS is what makes a domain name actually do something. Without DNS records, a domain is like a garage sale sign with no date, time or address on it, technically it exists, but it can’t send anyone anywhere.
Every essential service attached to your domain runs through DNS: your website loads because of it, your email arrives because of it, and your security and verification settings live in it.
How a DNS lookup works
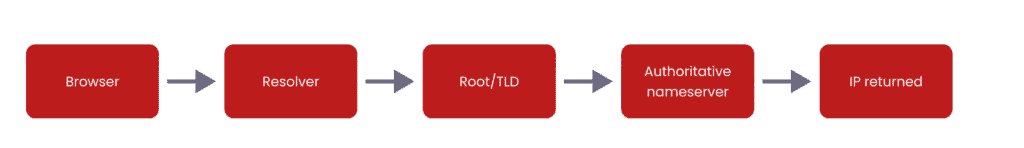
The whole process takes milliseconds and happens every time someone visits your site:
- You type a domain into your browser.
- Your device asks a DNS resolver (usually run by your internet provider) for the matching IP address.
- If the resolver doesn’t already have the answer cached, it queries the root and TLD servers to find out who’s in charge of that domain.
- It then asks that domain’s authoritative nameservers for the record it needs.
- The IP address comes back, your browser connects to the server, and the page loads.
Common DNS record types
A domain’s DNS zone is made up of individual records, each with a specific job. These are the ones you’ll come across most often:
| Record | What it does |
| A | Points your domain to an IPv4 address: the classic “where is my website” record. |
| AAAA | The same thing, but for a newer IPv6 address. |
| CNAME | Points one name at another name, creating an alias (e.g. www → your root domain). |
| MX | Directs incoming email to the correct mail servers. |
| TXT | Holds text information, used for SPF, DKIM, DMARC and domain verification. |
| NS | Names the authoritative nameservers responsible for the domain. |
| SOA | Holds administrative details about the DNS zone itself. |
| SRV | Specifies the server and port for a particular service. |
| CAA | Controls which certificate authorities are allowed to issue SSL certificates for your domain. |
| PTR | Used for reverse lookups, mapping an IP address back to a name. |
Two of these do a lot of heavy lifting for most businesses. Your MX records decide where your email lands: get them wrong and mail stops arriving. And your TXT records hold your email authentication, including your SPF record, which stops scammers spoofing your domain.
DNSSEC record types
DNSSEC (Domain Name System Security Extensions) adds a layer of cryptographic verification to DNS, so responses can be proven genuine rather than forged by an attacker. It relies on its own set of records:
| Record | What it does |
| DNSKEY | Publishes the public key used to verify signatures in the zone. |
| DS | The Delegation Signer record, which links your zone to the parent zone to establish a chain of trust. |
| RRSIG | The digital signature attached to a set of DNS records. |
| NSEC / NSEC3 | Proves that a particular record genuinely doesn’t exist, preventing forged “not found” replies. |
You’ll rarely edit these by hand. DNSSEC is usually enabled through your DNS provider, which generates and manages the records for you.
TTL and propagation: why changes take time
Every DNS record carries a TTL (Time To Live), a value in seconds telling resolvers how long to cache the answer before checking again. A TTL of 3600 means the record can be held for an hour.
That caching is why DNS changes aren’t instant. When you update a record, servers around the world may still be serving the old cached version until it expires. This delay is called propagation, and it typically takes anywhere from a few minutes to 48 hours.
A useful tip: if you know a change is coming, such as moving to a new host, lower the TTL a day or two beforehand. The change will then take effect much faster when you make it.
How do I manage my DNS?
Your DNS is managed wherever your nameservers point. You can check them with a free tool such as intoDNS.com, or by asking your provider.
When you register a domain, you can either supply your own nameservers or let it default to your registrar’s. From there you have a few options:
- Manage it with your registrar: most, including Domain Central, offer DNS management in their client portal.
- Use your hosting provider’s nameservers: handy if you want everything in one place.
- Use a third-party DNS service: some people prefer a specialist provider.
If you’re with Domain Central, you can manage your DNS records directly from your Client Area, and our Help Centre has a step-by-step guide. After changing nameservers, allow an hour or two for the update to take effect.
Frequently asked questions
What happens if my DNS records are wrong? Your website may not load and your email may stop arriving. DNS underpins both, so incorrect records break things quickly but they’re just as quickly fixed.
How long do DNS changes take? Usually minutes to a few hours, though it can take up to 48 hours. Lowering your TTL in advance speeds things up.
Do I need DNSSEC? It’s not mandatory, but it adds worthwhile protection against DNS spoofing, especially if you handle sensitive data or transactions.
Need a hand with your DNS?
DNS is powerful, but a single wrong record can take a website or email offline. If you have questions, or you’d like Domain Central to manage your DNS for you, submit a support ticket from your Client Area, our friendly Australian team is happy to help.