Few things are more unsettling than opening your inbox and finding a spam or phishing email that appears to come from your own address. Naturally, the first thought is: “Have I been hacked?”
In most cases, the answer is reassuring: no, you almost certainly haven’t. What you’re seeing is a trick called email spoofing, and while it looks alarming, it’s usually happening without any access to your account. In this guide we’ll explain why these emails appear, how to tell spoofing apart from a genuine account breach, and, most importantly, how to stop scammers using your domain.
The short answer: it’s spoofing, not hacking
Email was designed decades ago without much built-in security. As a result, the “From” address on an email is remarkably easy to fake, a bit like writing anyone’s name in the return-address corner of a posted letter. A scammer simply forges your address in the “From” field and sends the message from their own server.
They do this because email from a familiar sender (you) is more likely to be opened, trusted and acted on. It’s a classic phishing tactic and it doesn’t require your password at all.
Spoofing or a hacked account? How to tell
Before doing anything else, it’s worth ruling out a genuine compromise. Here’s how the two situations usually differ:
| Sign | Likely spoofing | Likely a hacked account |
| Where the email appears | Only in your inbox, from “you” | In your Sent folder as well |
| Contacts affected | A few random recipients | Many people in your address book |
| Login activity | Normal, no alerts | Unusual sign-ins or locked-out access |
| Password | Still works as expected | Suddenly changed or rejected |
If the messages only appear to come from you but there’s no trace in your Sent folder and your login still works normally, it’s almost certainly spoofing, not a breach.
If you do suspect a real compromise, act quickly: change your password to a strong, unique one, turn on two-factor authentication, review your account’s recent login activity, and check for any forwarding rules a scammer may have added.
How to stop scammers using your domain
Here’s the key point: you can’t stop a spammer from typing your address into the “From” field. What you can do is make it easy for the world’s mail servers to recognise those forgeries and reject them. You do this with three email authentication records that live in your domain’s DNS:
| Record | What it does |
| SPF | Lists which mail servers are allowed to send email for your domain. |
| DKIM | Adds a tamper-proof digital signature to every genuine email you send. |
| DMARC | Tells receiving servers what to do when a message fails SPF or DKIM. |
Used together, these three make it far harder for anyone to impersonate you and they also improve your own deliverability, so your real emails stop landing in recipients’ junk folders.
A closer look at DKIM
Of the three, DKIM (DomainKeys Identified Mail) is the one most people set up next after SPF, so it’s worth understanding.
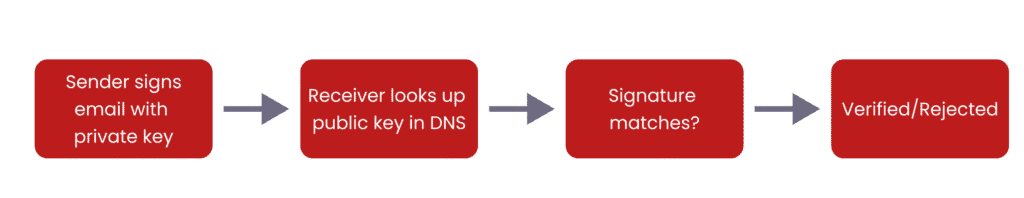
DKIM uses public-key cryptography to prove an email really came from you and wasn’t altered along the way. It works with a pair of keys:
- A private key, held securely by your sending mail server, which signs every outgoing message.
- A public key, published as a record in your DNS, which any receiving server can use to verify that signature.
Because only your server holds the private key, no one else can produce a valid signature for your domain. When a receiving server checks the signature against the public key in your DNS and it matches, the email is confirmed as authentic. If a scammer sends a spoofed message, it won’t carry a valid signature and that failure can be used to filter or reject it.
There are two parts to a DKIM setup: the DKIM record you add to your DNS, and the DKIM signature that’s automatically attached to the header of every email you send.
How to enable DKIM (and SPF and DMARC) for your domain
The good news is you rarely need to configure any of this by hand.
If your email is hosted with Domain Central, simply open a support ticket from your Client Area and we’ll enable DKIM for you. If we manage your DNS, we’ll switch it on directly; if someone else manages your DNS, we’ll supply the exact records for you to pass along.
If your email is hosted elsewhere, contact your email provider and ask them to enable DKIM (and confirm your SPF and DMARC records are in place). Not sure who your provider is? Open a ticket with us and we’ll help you find out.
Can I stop the spoofed emails reaching my own inbox?
Partly. Authenticating your domain mainly protects other people from being fooled and boosts your deliverability. To have spoofed messages actively rejected or quarantined before they reach inboxes, including your own, you need a DMARC record set to an enforcement policy. That’s the piece that instructs mail servers to bin anything that fails the checks. It’s the final layer on top of SPF and DKIM, and it’s what turns “we can detect fakes” into “we automatically block them.”
Frequently asked questions
Does getting spam from myself mean I’ve been hacked? Usually not. It’s almost always spoofing: a forged “From” address sent from someone else’s server, with no access to your account.
Will deleting the email or changing my password fix it? Changing your password is smart if you suspect a breach, but it won’t stop spoofing on its own. The lasting fix is authenticating your domain with SPF, DKIM and DMARC.
Do small businesses really need all three records? Yes. Since 2024, major providers like Gmail and Yahoo effectively require authentication, and a properly protected domain is far harder to impersonate.
We can set this up for you
Worried about spoofed emails or messages landing in spam? Domain Central can configure SPF, DKIM and DMARC so your domain is protected and your emails get delivered. Open a support ticket from your Client Area or get in touch, our friendly team is happy to help.